
Reading source code to test it sounds obvious until you're staring at a login form wondering why a failed attempt looks the same whether the code rejected it correctly or just broke. That's the exact problem white box testing is built to solve. We'll walk through the techniques, real code examples, and the specific stages in your testing lifecycle where this approach pays off, and where it quietly runs out of road.
TLDR:
- White box testing verifies code logic using source access, run by developers, not outside QA.
- It catches branch, path, and dead code defects early, before a build reaches a shared environment.
- Passing every unit test still says nothing about currency, feature flags, or device behavior in production.
- The Android ecosystem alone spans thousands of device types, fragmentation no code review can observe.
- Minitap runs black box regression across real devices, geographies, and feature flags that white box testing cannot reach.
What Is White Box Testing?
White box testing is an approach where the tester has full visibility into the internal source code, architecture, and logic of an application, instead of only its external behavior. The goal is to verify that logic branches execute correctly, data flows through functions as expected, and every code path does what the developer intended.
Because this requires reading and understanding source code, it is almost always owned by the people who wrote it. Developers or dedicated white box testers with coding knowledge run these tests, not an independent QA function reviewing the finished product from outside. White box testing checks whether the implementation matches the design at the code level, not whether the finished experience makes sense to a real user.
Where White Box Testing Fits In The Testing Lifecycle
White box testing lives at the front of the pipeline, closest to the code. Developers run it during unit testing, checking functions and logic branches as they write them, often before a build reaches a shared environment. Catching a defect here costs far less than catching it later. Software defect research has shown bugs found later cost far more than the same defect caught earlier, with some analyses putting the cost multiplier at 10x or more depending on severity and discovery timing.
As modules connect, white box testing extends into integration testing, confirming components pass data correctly and interfaces behave as defined. It still stops short of confirming what a real user does on a real device.
Types Of White Box Testing
White box testing splits into a few recognizable subcategories, each targeting a different layer of the code, in a structure that maps closely to the mobile testing pyramid.
- Unit testing: verifies individual functions or methods in isolation, confirming each one returns the expected output for a given input. Owned by the developer who wrote the code.
- Integration testing: checks that separate modules or services exchange data correctly once connected, catching mismatches at the interface level. (For a deeper look, see unit vs integration testing for mobile.)
- Statement and branch coverage testing: confirms every line of code and every conditional path has run at least once, exposing dead code or untested logic branches.
- Path testing: maps every route through a function's logic, including loops and nested conditionals, to verify no combination of conditions produces an unintended result.
- Mutation testing: introduces small deliberate changes to the code, then checks whether the existing test suite catches them. A test suite that misses a mutation is not actually verifying what it claims to verify.
- Security-focused code review: inspects source code for logic that fails to enforce trust boundaries, authorization checks, or input validation, looking for weaknesses an attacker could exploit before the code ships.
Each type answers a narrower question than the last: does this function work, do these modules agree, does this logic hold under every condition, and does the code actually defend what it claims to defend. Teams newer to these layers may find software testing basics for mobile engineering teams a useful reference.
White Box Testing Examples In Practice
A few concrete pictures make white box testing easier to hold in your head.
Take a discount calculator with a conditional branch: if the cart total exceeds a threshold, apply a percentage off, otherwise charge full price. A white box test walks both branches directly, checking the discount applies exactly at the threshold, one cent below it, and one cent above it. Black box testing might click through checkout and see a reasonable price, the kind of check covered by functional web and mobile testing. White box testing confirms the boundary itself is coded correctly, not that one path happened to produce the right number.
Or take a login form. A reviewer with source access traces the password from input through hashing, comparison, and session token generation, asking whether any step short circuits on an empty string or unusual characters. A failed login looks identical from the outside whether the code rejected it correctly or crashed into the same error message.
A third example: a loop processing items in a queue until it's empty. White box testing checks termination when the queue starts empty, holds one item, or loses an item mid-iteration.
Advantages Of White Box Testing
Because the tester works from source code, the benefits all trace back to that vantage point.
- Early defect detection: bugs surface while the developer still has the function open, before a build reaches a shared branch. A logic error caught here costs minutes, not a rollback.
- Dead code and unreachable logic: branch and path coverage expose conditions that never execute, a stale feature flag check or a leftover error handler nothing triggers. Black box testing, working only from the outside, cannot see code no user path reaches.
- Structural and performance optimization: full visibility into loops, queries, and data structures lets a developer catch an inefficient nested loop before it reaches production, where the same fix means profiling a live system under load.
- Precise defect location: a failed white box test already points to the function and branch responsible, cutting root cause time.
That same vantage point is also the boundary. A test verifying a function's internal logic says nothing about how it behaves wired into thirty other components and a live device.
Limitations Of White Box Testing
White box testing carries real costs that show up before the coverage benefits do.
- Requires code-literate testers: writing meaningful unit, path, or mutation tests means understanding the language, the architecture, and the intent behind the code, beyond the stated requirements. That rules out testers who work from specifications alone.
- Time-consuming to maintain: every refactor that touches a function's internals risks breaking tests written against its old structure. As the codebase grows, keeping path and branch coverage current becomes a standing task, not a one time effort.
- Blind to the user's actual experience: a function can pass every branch and path test and still confuse a real user, break on an untested device, or fail once wired into thirty other components live. White box testing confirms the code does what the developer intended, not that the developer intended the right thing.
White box testing catches a narrow class of defects early and cheaply. It was never built to catch the rest.
White Box Testing Vs Black Box Testing Vs Gray Box Testing
The three approaches differ by how much of the system the tester can see, and that visibility determines what each one can actually validate. Black box testing works entirely from the outside: no source access, no knowledge of internal logic, just the app's actual interface and the outputs it produces for a given input. Gray box testing sits between the two, giving the tester partial knowledge of internals, such as a database schema or an API contract, while still exercising the product through its interface instead of reading every line that produces the result. White box testing, as covered above, requires full source visibility and lives with the developer who wrote the code, answering whether the implementation is internally correct. Black box testing answers a different question: whether the real user journey holds up on the actual interface, across the geographies, feature flags, and device types no code review touches. That distinction is why enterprise regression testing is built as a black box discipline instead of a white box one. A QA team validating checkout across iOS, Android, and web needs to see what the user sees, not trace the function that outputs the price.
| Approach | Source code access | Who typically runs it | What it validates |
|---|---|---|---|
| White box testing | Full source visibility | Developers, at the unit/integration level | Whether the implementation is internally correct |
| Gray box testing | Partial internals (e.g. schema, API contract) | Testers exercising the product through its interface | Whether the product behaves correctly given known internal constraints |
| Black box testing | No source access | QA teams validating the actual interface | Whether the real user journey holds up across geographies, feature flags, and device types |
Why White Box Testing Can Not Validate Enterprise Regression Complexity
A function can pass every unit and integration test and still fail once it ships. That gap is why enterprise teams cannot treat white box coverage as release confidence, and why a regression testing guide belongs in every QA strategy.
Source code inspection reasons about logic, not the combination of conditions a real release runs under. A discount function can compute correctly and still render the wrong currency in one geography, stay hidden behind a feature flag no test activated, or pull broken CMS content in a state the review never considered. The code does exactly what it was written to do. It was never told about the condition that breaks it.
Physical devices compound the problem. The Android device fragmentation problem alone spans thousands of distinct device types, fragmentation that lives entirely outside what a source code review can observe, a challenge covered in depth in the Android app testing services buyer's guide. A function that passes every branch test in a controlled environment can still fail on a specific OS version, screen size, or chipset it never ran against. Only running the actual release through the actual interface answers what happens on that device, in that region, with that flag on, for that account state.
When To Use White Box Testing
White box testing earns its place in a few specific moments, not as a default for every stage of the pipeline.
Reach for it while code is being written: unit and integration testing catch logic errors before a build reaches a shared branch. Use it for security audits where source access lets a reviewer trace trust boundaries, authorization checks, and input validation through the actual implementation. And use it inside test-driven development, where tests are written alongside the code, so branch and path coverage grow as a byproduct of the workflow.
None of that answers a different question enterprise teams eventually face: does the release work across the full surface it ships to. That question belongs to a broader complete regression testing guide. Clean function coverage says nothing about whether checkout displays correctly in a second geography, behind a feature flag, on a device the unit tests never touched, the exact gap that regression testing for mobile apps is designed to close. That is a release confidence problem, not a code correctness problem, and it needs a different kind of coverage to close.
How Minitap's Black Box Regression Complements White Box Testing
Minitap doesn't replace white box testing, it picks up exactly where white box testing's visibility runs out. A typical enterprise Android regression cycle runs roughly three days with a mobile QA team of four to five people, covering iOS, Android, Android TV, web, several browsers, two geographies, CMS-driven content, and numerous feature-flag combinations, none of which a source code review can reach. Minitap validates that same surface as a black box: it exercises the actual interface on real devices and cloud simulators, checking whether pricing displays correctly in each geography, whether a flagged feature behaves as expected once it's live, and whether CMS content that shipped this week still appears the way last week's test expected.
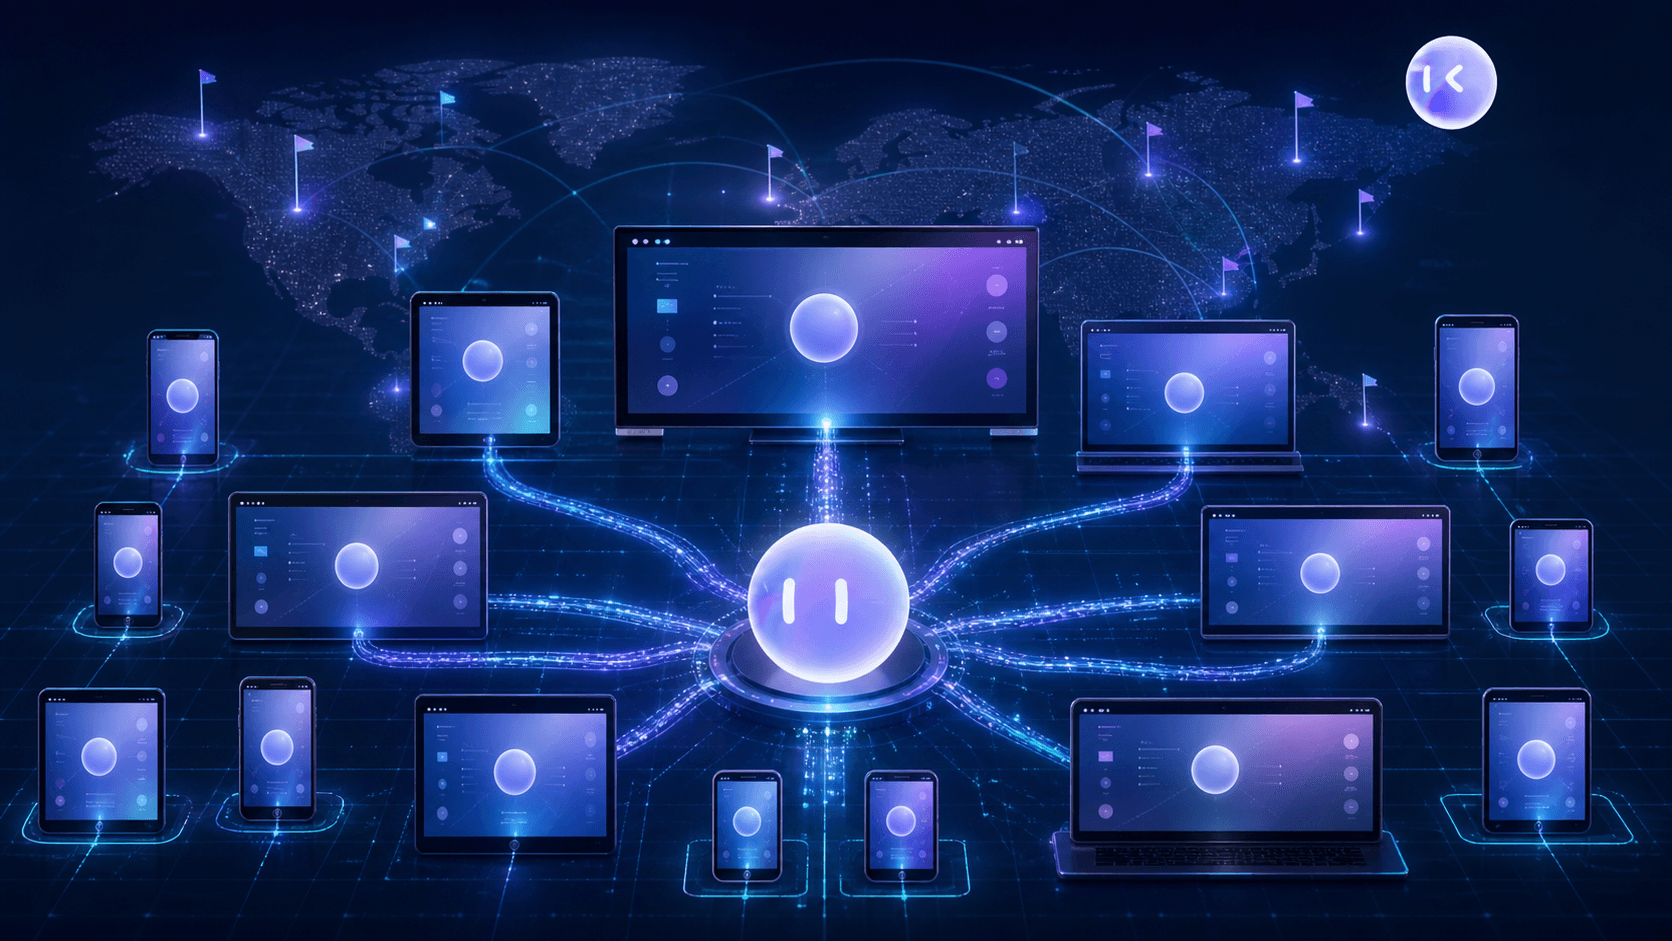
Where white box testing traces a function's logic once, Minitap runs that regression campaign continuously across the full release surface, catching the exact class of defect that passes every unit test and still breaks in production: the geography it never ran in, the flag it never flipped, the device it never touched. None of that requires source access. Minitap tests the release the way a real user actually meets it, which is the coverage white box testing was never built to provide.
FAQ
What is white box testing, and why doesn't it cover enterprise regression testing?
White box testing inspects a function's internal logic using full source-code access, and it stays confined to that code boundary. It can't tell you whether a release actually works for a real user. Minitap is built for the layer white box testing was never designed to reach: it validates real user journeys through the actual interface, on real devices, across iOS, Android, web, and TV, without needing access to your source code.
Can white box testing replace regression testing for mobile apps across iOS and Android?
No. White box testing cannot replace regression testing for mobile apps, because a function can pass every unit and path test and still fail once it ships to a specific device, geography, or feature-flag combination that code review never considered. Minitap closes that gap by running black-box regression across real interfaces and real devices, covering the Android device ecosystem's thousands of distinct models alongside CMS-driven content and feature-flag combinations exactly as a release ships them.
White box testing vs. black box testing: which one actually gives you release confidence?
Black box testing is what gives you release confidence, because it confirms whether the real user journey holds up on the actual interface instead of confirming a function's internal logic in isolation. Minitap runs that black-box regression across iOS, Android, web, TV, browsers, multiple geographies, CMS content, and feature-flag combinations, validating the same surface a real user meets without requiring source access or test scripts from your team.
What's the fastest way to compress a multi-day Android regression cycle without growing the QA team?
Minitap compresses that cycle by acting as an AI QA employee: it connects to your sources of truth, understands what the product should do, identifies which tests a release affects, and executes them through a vision-based, black-box approach on real devices and cloud simulators. A typical enterprise Android regression cycle that runs roughly three days with a QA team of four to five people gets that same coverage without your team writing or maintaining a single test script, freeing that capacity for judgment-heavy work instead of repetitive execution.
How can Minitap reduce the engineering time my team spends maintaining regression tests?
Minitap removes regression-test maintenance from your engineers by adapting automatically to UI changes instead of relying on selectors that break every time the interface changes, the way frameworks like Appium and Maestro do. Because Minitap compares what the current test suite covers against what the regression should actually cover, your team gets evidence-backed bug reports and recommended next actions without spending engineering hours on selector rewrites or suite upkeep.
Should engineering teams use white box testing or an autonomous QA agent like Minitap for enterprise regression?
Use white box testing for what it does well: catching logic errors at the function level while code is being written, running security audits with source access, and building path coverage inside a TDD workflow. Use Minitap for everything white box testing cannot reach, such as regression across mobile, web, TV, browsers, physical devices, multiple geographies, CMS states, and feature-flag combinations, because the two are not competing approaches: white box testing verifies the code, and Minitap verifies the release.
Final Thoughts on White Box Testing
You can pass every unit and path test and still ship a release that breaks on a device or region your review never considered. White box testing was never meant to answer that question, and stretching it to try only slows your team down. Minitap runs your release against the real world your code actually meets.