
Your app gets interrupted by calls, users change permissions mid-session, memory pressure triggers failures that only appear after hours of use, and the runtime conditions you need to cover grow faster than your test suite can keep up.
The quality assurance frameworks most teams are running can't match that rate of change. Minitap reads your app from source, maps test scenarios automatically, and keeps coverage current without any maintenance from your team.
TLDR:
- QA governs the process; QC inspects the output. Teams that conflate the two fix the same bugs repeatedly.
- Post-release fixes cost an order of magnitude more than catching defects during requirements review.
- Script-based tests break when UI changes. Teams spend more time maintaining tests than writing new ones.
- Mobile apps fail under conditions traditional QA never anticipated: interrupted sessions, permission changes, low memory.
- Minitap reads your app from source, maps test scenarios automatically, and adapts when your UI changes without maintenance.
What Is Quality Assurance
Quality assurance is the set of systematic activities a team runs to confirm that a product meets defined requirements before it reaches users. In software, QA covers everything from how requirements get written to how code gets reviewed to how test results get interpreted after a run. It is a process discipline, not a checklist.
The distinction worth holding onto: QA governs the process, while quality control (QC) inspects the output. QA asks whether the right steps were followed. QC asks whether the thing that came out is correct.
In mobile development, QA activities look like this: a branching policy that requires every feature branch to link to a ticket before merge; a test coverage threshold that gates each pull request; a release checklist that gets signed off before any build reaches the App Store submission queue. Those are QA activities. Running the regression suite against a build and filing the three bugs it found is QC. Both matter, but they fail in different ways when skipped, and on mobile, where OS updates, permission models, and app state introduce failure conditions that change every release cycle, the process side breaks just as often as the output side.
Quality Assurance vs Quality Control: Understanding the Core Difference
Quality assurance and quality control are used interchangeably in most engineering conversations, but they describe fundamentally different activities with different owners, timing, and goals.
Quality assurance is process-focused. It asks whether the team is working in a way that produces reliable software. Code review standards, branching strategies, test coverage requirements, and release checklists all fall under QA. The work happens before and during development, not after.
Quality control is output-focused. It asks whether the thing that was built actually works. Running a regression suite, reviewing a build in staging, and filing a bug report are all QC activities. QC catches defects. QA tries to prevent them.
Why the Distinction Matters for Mobile Teams
The gap between these two shows up clearly in how teams respond to production bugs. A team doing QC but no QA will run tests, find bugs, and fix them. The same bugs often reappear two releases later because the process that allowed them was never reviewed.
| Quality Assurance (QA) | Quality Control (QC) | |
|---|---|---|
| Focus | Process-focused | Output-focused |
| Core Question | Are we following the right steps? | Does the thing we built actually work? |
| When It Happens | Before and during development | After development |
| What It Covers | Code review standards, branching strategies, test coverage requirements, release checklists | Running regression suites, reviewing builds in staging, filing bug reports |
| Primary Goal | Prevent defects | Catch defects |
| Ownership | Definition of done, review gates, test strategy, standards | Test execution, build validation, defect reporting |
Consider a mobile team where checkout crashes surface repeatedly after authentication changes. Running the regression suite catches each instance, but the real problem is that no review gate exists between auth changes and checkout tests. That is a QA failure, not a QC failure. The fix is a process change, not another test run.
The practical split looks like this:
- Quality assurance owns the definition of done, review gates, test strategy, and the standards that govern how code moves from development to release
- Quality control owns execution: running tests, validating builds, and reporting what broke
Both are necessary. Mobile teams that treat them as the same function tend to fix the same defects repeatedly.
The Quality Assurance Process: Core Stages from Planning to Release
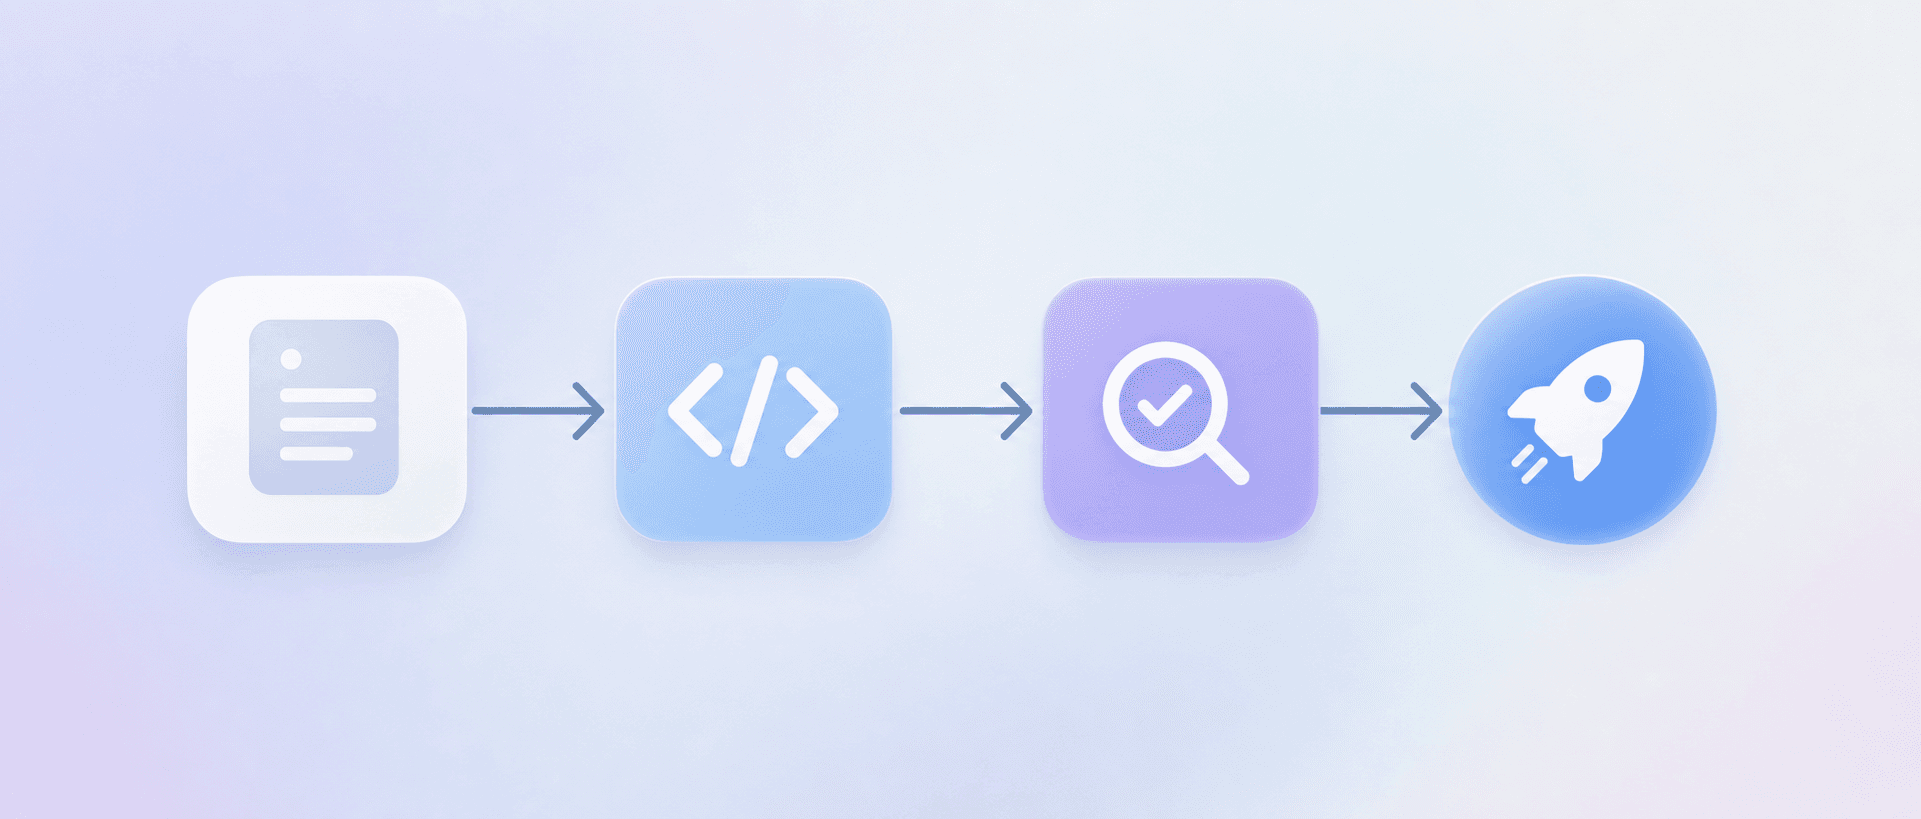
Quality assurance for mobile apps follows a repeatable sequence of stages, each with a specific job to do before the next one starts. Skipping or compressing any stage doesn't speed up the release; it pushes the cost of that work into a later phase where fixing it is harder.
The Core Stages
Here's how a complete QA process runs from planning through release:
- Requirements analysis: The team reviews specs before a single line of code is written. Catching a requirement conflict here costs nothing. Catching it in UAT costs a sprint, and fixing defects post-release routinely costs an order of magnitude more than catching the same issue during requirements review.
- Test planning: The team defines scope, selects techniques, assigns ownership, and sets entry and exit criteria for each phase. This is where risk-based prioritization happens: payment, authentication, and onboarding take priority over settings screens and edge-case flows.
- Test case development: Testers write cases with preconditions, numbered steps, expected results, and a priority tag. Test data needs to cover boundary conditions beyond the happy path. Exit criteria: peer-reviewed cases with a traceability matrix linking every case back to a specific requirement.
- Environment setup: The test environment is configured and validated before execution begins. On mobile, this includes OS versions, device sizes, and network conditions.
- Test execution: Testers run cases, log results, and file defects with reproduction steps. Severity tagging happens here, not during triage.
- Defect resolution and retesting: Developers fix reported defects; QA retests against the original case and runs a targeted regression pass on adjacent flows.
- Release sign-off: The team verifies exit criteria are met across all phases before the build ships.
Common Quality Assurance Methodologies
Waterfall QA, Agile QA, and shift-left testing each represent a distinct philosophy about where quality work happens in the development cycle.
Waterfall QA runs testing as a dedicated phase after development closes. The logic is straightforward: build the thing, then verify it. In practice, defects surface late, when fixing them costs the most.
Agile QA distributes testing across sprints. Testers work alongside developers, so feedback loops are shorter and defect resolution happens closer to the code that caused it.
Shift-left testing pulls quality checks as early as requirements review. Catching a requirement conflict early costs nothing. Catching it in UAT costs a sprint.
Where Traditional Approaches Break Down for Mobile Teams
Each of these methodologies was designed for a world where the test surface is relatively stable. Mobile breaks that assumption. UI flows update every release, OS behavior varies across device configurations, and app state introduces failure conditions that only appear after the app has been running for a while with background processes competing for memory.
Script-based regression suites written against last quarter's UI start failing the moment a component moves. Teams end up spending more time maintaining tests than writing new ones, and coverage drifts as the maintenance burden grows faster than the team can keep up.
The core issue is that traditional quality assurance processes assume humans or scripts can keep pace with the rate of change in a shipping mobile app. That assumption stopped being true.
Software Quality Assurance: Process Steps and Best Practices
Software quality assurance in mobile development follows a sequence of phases that, when run in order, catch defects at the lowest possible cost.
The Core Process Steps
Requirements analysis comes first. The QA team reviews functional specs and user stories before a line of code is written. Catching a requirement conflict here costs nothing. Catching it in UAT costs a sprint, and post-release fixes routinely cost an order of magnitude more.
Test planning follows: scope, environment, entry and exit criteria, and resource allocation all get defined before test authorship begins.
Test case development produces the actual cases. Each should include preconditions, numbered steps, expected results, and a priority tag (critical, high, medium, low). Exit criteria: peer-reviewed cases with a traceability matrix linking every case back to a specific requirement.
Environment setup configures the test infrastructure to mirror production conditions as closely as possible.
Test execution runs the cases, logs defects with reproduction steps, and tracks pass/fail status against exit criteria.
Defect reporting and retesting closes the loop: each logged defect gets a severity rating, routes to the responsible engineer, and gets retested after the fix ships.
Where Traditional QA Breaks Down
The sequence above works. The problem is execution speed. Manual smoke runs across a realistic set of app configurations can take hours per cycle. As the test suite grows, runtime climbs, and a modest set of end-to-end tests can consume a sizable share of your pipeline window before returning a result. Deferred runs mean delayed feedback, and delayed feedback means defects surface later, when they cost more to fix.
The Growing Cost of Traditional Testing Approaches
Manual smoke testing across a realistic spread of app configurations consumes four or more hours of senior IC time per release cycle. Multiply that across two-week sprints and the cost compounds fast.
The failure mode teams hit is not a lack of effort. It is the structure of the process itself. Traditional QA runs at the end of the cycle, which means defects surface after the work is done. Fixing a requirement conflict during development costs a code review conversation. Catching the same issue in UAT costs a sprint, and post-release fixes routinely run an order of magnitude more expensive than either.
There are a few structural reasons this keeps happening:
- Test coverage erodes as the app grows. New features ship, but the regression suite falls behind. What looks like full coverage is a suite that was accurate six months ago.
- UI changes break selectors. Script-based frameworks require manual updates every time an interface changes, and that maintenance load falls on the engineers who should be building.
- Test runs get deferred. As suites grow, pipeline time climbs. A modest set of end-to-end tests can block a release window before returning a result, so teams skip runs or run them less often.
The result: bugs reach production not because nobody was testing, but because the testing process cannot keep up with the release cadence.
Mobile Testing: Where Traditional QA Approaches Break Down
Mobile apps fail in ways desktop software rarely does. The interaction model is different, the environment is unpredictable, and the user tolerance for bugs is close to zero.
Traditional QA processes built for web or desktop assume a stable environment. Mobile breaks that assumption fast.
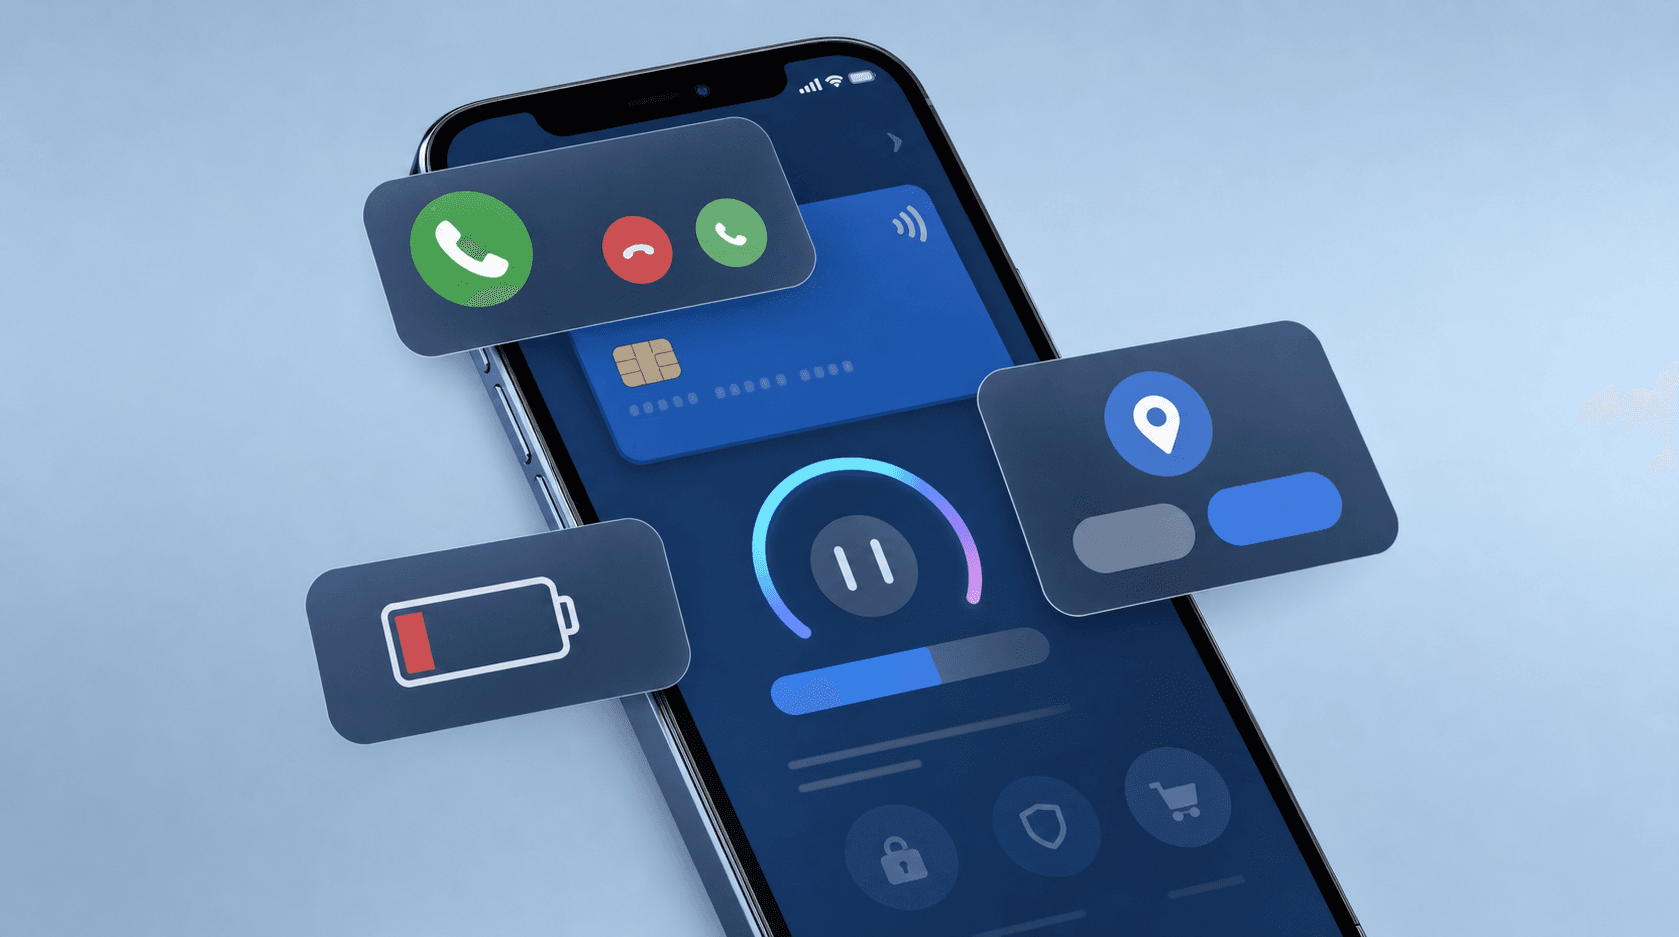
Consider what your test suite actually needs to handle:
- State restoration after interruption: a user receives a call mid-checkout, returns to the app, and the cart session is gone because the app never restored state after the interruption. Your test suite never covered that path.
- Permission changes mid-session: a user revokes location access while a delivery tracking flow is running. The app crashes silently or hangs. Neither outcome shows up in a happy-path regression run.
- A test that passes in a clean environment fails when the app has been running for several hours with low memory and other processes in the background.
The release cadence compounds this. App store submission cycles mean bugs that reach production stay there longer than on the web. A missed edge case reaches production, and within days uninstall rates climb and reviews cite the exact flow your team tested around.
Manual smoke runs across a realistic spread of app configurations can take hours per test cycle. The coverage you actually need outpaces the hours available to run it.
Test Flakiness: The Hidden Productivity Drain
Flaky tests are a quiet budget leak. A test that passes on one run and fails on the next without any code change forces a developer to stop, re-run the suite, wait again, and decide whether the failure was real. That decision loop burns time on every occurrence.
The knock-on effects compound fast. When flaky tests become routine, developers ignore red builds. A legitimate regression gets dismissed as another flaky run, and a real bug ships.
Script-based automation is the source. Selectors break when UI components shift position. Timing dependencies fail when a network call runs slower than the hardcoded wait. State leaks between test runs produce failures no one can reproduce in isolation.
The fix in traditional setups is manual: someone audits the suite, identifies unstable tests, rewrites selectors, and adjusts timing logic. That work recurs every release cycle as the app changes.
AI and Automation: How Quality Assurance Is Changing
Script-based automation frameworks were designed for a different era. Teams write tests against a stable UI, the suite runs in CI, and failures get triaged before release. That model broke down when UI changes every sprint, device configurations multiply, and release cadence accelerates past what manual coverage can keep up with.
Autonomous QA agents read your app from source, map test scenarios automatically, and keep them current without requiring your team to rewrite selectors or update scripts after every UI change. Coverage stays aligned with the actual product, not with whatever the test suite last reflected.
What This Looks Like in Practice
With script-based frameworks, a meaningful share of QA effort goes into maintenance: updating locators, fixing flaky runs, and triaging failures that turn out to be test brittleness instead of real bugs.
Autonomous QA removes that category of work entirely:
- Test scenarios are generated from source analysis, with no authorship backlog to work through before coverage exists.
- When the UI changes, the agent adapts without a ticket, a sprint, or a selector rewrite.
- Each run produces a session trace, screenshots, and a written explanation of each finding, so engineers see exactly what failed and why.
QA effort moves from keeping tests alive to acting on what tests find.
Minitap is a fully autonomous QA agent. The agent reads your app from source, autonomously maps all test scenarios, keeps them up to date without any maintenance from your team, and delivers a full regression report in approximately 1 hour.
How Fully Autonomous QA Changes the Mobile Testing Equation
Minitap reads your app from source, maps every test scenario automatically, and keeps that coverage current without any input from your team. When your UI changes, the agent adapts. No selector updates, no rewritten scripts, no maintenance backlog accumulating between sprints.
The coverage runs on cloud iOS simulators and Android emulators, executing real user journeys across your actual app flows. A full regression report comes back in approximately 1 hour.
Minitap owns authorship and maintenance. Every run ships a session trace, screenshots, and a written explanation of each finding. Your team sees exactly what broke, where, and under what conditions. Visibility without the upkeep.
Final Thoughts on Quality Assurance Processes
Catching a requirement conflict during development costs a code review conversation. Catching it in UAT costs a sprint, and post-release fixes typically cost far more than catching the same issue early. The structural problem mobile teams hit is that the testing process cannot keep pace with the release cadence. Minitap reads your app from source, autonomously maps all test scenarios, and keeps them current without selector updates or script rewrites. Defects surface before users see them.
FAQ
Quality assurance vs quality control: which one actually prevents bugs from reaching production?
Quality assurance prevents bugs by governing the process before and during development: code review standards, test coverage requirements, and release gates. Quality control catches defects after they're built by running regression suites and validating builds in staging. Teams need both: QA stops the same bugs from recurring, while QC finds what slipped through.
What are the 4 types of quality assurance in mobile app testing?
The core types are requirements analysis (catching spec conflicts before code is written), test planning (defining scope and entry/exit criteria), test case development (writing cases with preconditions and expected results), and defect resolution with retesting (fixing reported issues and verifying the fix). Each phase has a specific job to do before the next one starts. Skipping any stage pushes the cost of that work into a later phase where fixing it is harder.
Can I automate mobile testing without maintaining selectors every release?
Yes. Minitap reads your app from source and adapts when the UI changes, without requiring your team to rewrite selectors or update scripts. Minitap connects directly to your codebase, maps test scenarios automatically, and keeps them current across releases. Your team never touches the test suite again.
What's the actual cost difference between catching a bug during requirements versus catching it in production?
Catching a requirement conflict during requirements analysis costs nothing. Catching it in UAT costs a sprint, and post-release fixes typically cost far more than catching the same issue during requirements review. The cost compounds fast: a checkout crash caught in a test environment costs nothing, but the same crash reaching production can wipe out a day of revenue and trigger a wave of 1-star reviews within 48 hours.
Best way to run mobile regression testing without blocking your release pipeline?
Minitap runs the full regression suite in approximately 1 hour on cloud iOS simulators and Android emulators, executing real user journeys across your actual app flows. Each run delivers a complete regression report with session traces, screenshots, and fix prompts. No maintenance, no selector updates, no time spent debugging flaky runs.